The most dangerous part of this attack is that hackers did not need a software vulnerability. They borrowed the trust of a verified HBO Max account and persuaded users to run the malware themselves.
Hackers compromised an HBO Max account authorized to advertise on Reddit and used it to distribute malicious ads that directed Mac and Windows users to fake download pages employing a social-engineering technique known as ClickFix.
Cybersecurity researchers at Hudson Rock said the compromised account pushed 108 separate ads over roughly 48 hours, including fake HBO Max downloads as well as lures targeting users looking for AI tools and Mac utilities. The campaign formed part of a broader cross-platform malware operation researchers are calling PasteSwitch.
Reddit told TechCrunch that it locked the compromised account and removed the affected advertisements. The company has not disclosed how many Reddit users saw, clicked or were ultimately infected through the campaign.
Key Facts
| Detail | Information |
|---|---|
| Attack | ClickFix malvertising campaign |
| Platform | |
| Compromised account | Verified HBO Max account |
| Malicious ads identified | 108 |
| Main targets | macOS and Windows users |
| Campaign name | PasteSwitch |
| macOS threats | MacSync, AMOS and related credential-stealing payloads |
| Windows threat | Amatera Stealer and related loaders |
| Reddit response | Account locked and malicious ads removed |
| Confirmed victim count | Unknown |
How Did the Fake HBO Max Reddit Ads Work?
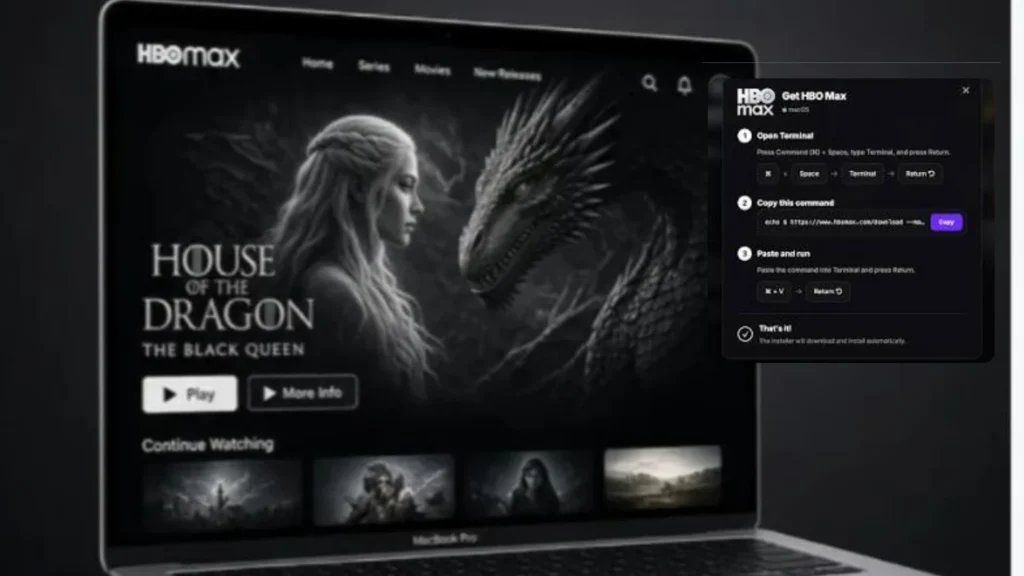
Researchers traced the campaign after Reddit users spotted advertisements apparently posted by the verified HBO Max account promoting a native HBO Max app for macOS.
The advertisement sent users to a convincing website designed to resemble legitimate HBO Max branding. Instead of providing a normal application download, however, the page displayed instructions telling users to copy and paste a command into their computer.
That is the central trick behind a ClickFix attack.
Rather than exploiting a browser or operating-system vulnerability directly, ClickFix persuades the victim to execute an attacker-supplied command through tools such as Terminal on macOS or PowerShell and other command interfaces on Windows.
Microsoft has documented similar ClickFix campaigns in which fake downloads, verification pages and CAPTCHA-style prompts persuade users to execute commands that retrieve information-stealing malware.
What Malware Could the ClickFix Campaign Install?
Hudson Rock’s investigation found that the PasteSwitch infrastructure could change what it delivered depending on the victim’s operating system.
On macOS, researchers identified malware including MacSync and Atomic macOS Stealer-related components, which can target browser credentials, passwords, cryptocurrency wallet information and other sensitive data.
Windows users could instead be routed through a different infection chain involving PowerShell and an information-stealing threat known as Amatera Stealer.
Researchers also identified cryptocurrency-focused malware capable of replacing wallet addresses copied to the clipboard, potentially redirecting transactions to an attacker-controlled address.
Does Clicking the Fake HBO Max Ad Automatically Infect Your Computer?
Based on the infection chain documented by researchers, simply seeing or opening the advertisement was not the critical malware-execution step.
The ClickFix technique depended on users following the malicious website’s instructions and then pasting and running the supplied command on their Mac or Windows PC.
That distinction matters for anyone who remembers clicking one of the suspicious HBO Max advertisements but did not run anything afterward.
Microsoft describes ClickFix as a social-engineering attack that relies on convincing the target to execute malicious instructions rather than silently exploiting the computer in the background.
Why Does This Attack Matter?
The HBO Max campaign demonstrates why ClickFix attacks can be unusually convincing.
Users are routinely warned to avoid suspicious accounts and unknown advertisers, but this campaign used an established brand’s verified Reddit identity. That removed one of the warning signs people normally rely on when deciding whether an advertisement is trustworthy.
The technique also turns normal operating-system tools into part of the infection process. Instead of asking users to open an obviously suspicious executable, attackers tell them to run a command themselves.
Microsoft says this approach can sidestep parts of the normal application-download security process on macOS because execution begins through Terminal rather than a conventional downloaded application.
Who Should Be Concerned?
The highest-risk group is Mac or Windows users who encountered one of the malicious advertisements and copied, pasted and executed the command provided by the linked website.
Users who entered passwords after executing the command, stored passwords in their browser, remained logged in to important online accounts or used cryptocurrency wallets on the affected computer should treat the incident particularly seriously because information-stealing malware is designed to collect those types of data.
Microsoft says modern macOS infostealers can target browser credentials, saved passwords, cryptocurrency wallets, cloud credentials and developer secrets.
What Should You Do If You Ran the ClickFix Command?
- Disconnect the affected computer from the internet while investigating it to limit additional communication with attacker infrastructure. Run a full malware scan using trusted security software and make sure the operating system and security tools are fully updated.
- Use a different, known-clean device to change important passwords, beginning with your primary email account, password manager, financial accounts and other services containing sensitive information. Where available, sign out other active sessions and enable multi-factor authentication.
- Treat exposed cryptocurrency credentials with extra caution. If wallet recovery phrases, private keys or wallet information may have been accessible on the infected computer, consider those secrets potentially compromised and follow the wallet provider’s security guidance.
- Do not paste commands supplied by websites into Terminal, PowerShell, Command Prompt or the Windows Run dialog unless you fully understand and trust the command. Microsoft specifically warns that legitimate downloads and CAPTCHA or verification checks should not require users to paste commands into Terminal.
Sebertech Analysis
What makes this incident notable is not a new zero-day or an unusually sophisticated exploit. It is the combination of a trusted advertising identity, polished brand impersonation and a technique that persuades users to bypass security barriers themselves.
The compromised HBO Max account gave the attackers something that ordinary malicious advertisements usually lack: credibility.
The 108-ad burst also shows that the HBO Max lure was only one part of the operation. Hudson Rock found ads impersonating streaming software, AI tools and Mac utilities, suggesting the attackers were testing multiple themes while the compromised advertising account remained usable.
For users, the simplest warning sign is therefore not the brand shown in the advertisement. It is the instruction that follows. A website asking you to open Terminal, PowerShell or another command tool and paste text into it should be treated as a major security warning regardless of how legitimate the page appears.
What Is Still Unknown?
Researchers and Reddit have not disclosed how the HBO Max advertising account was initially compromised.
The total number of Reddit users who were shown the malicious advertisements is also unknown, as is the number who followed the instructions far enough to infect their computers.
There is also no public attribution identifying the individual or group operating PasteSwitch.
Those gaps make it impossible to determine the campaign’s full impact at this stage.
What Happens Next?
Reddit has removed the malicious advertisements and secured the affected account, but ClickFix itself remains an active threat technique.
Researchers have documented attackers rotating domains, changing lures and adapting delivery infrastructure, meaning blocking one fake HBO Max website will not eliminate the broader risk.
Users should remain particularly suspicious of advertisements, fake downloads, CAPTCHA pages or troubleshooting instructions that ask them to paste commands into their operating system’s command-line tools.
Source:
- Microsoft Security: From Open Lures to Cloaked Gates: How a macOS ClickFix Campaign Learned to Hide
Written by Liam Hisona
Published: September 15, 2026, 9:30 AM PHT
